By Herbert Boyles September 24, 2026
Yes. A field-service company can store a customer’s card for authorized future charges, but the customer must agree before the credential is stored or used. The agreement should explain how future amounts are determined, what triggers charging, and cancellation/refund terms; the setup authorization or account verification and later merchant-initiated transactions must also be identified correctly.
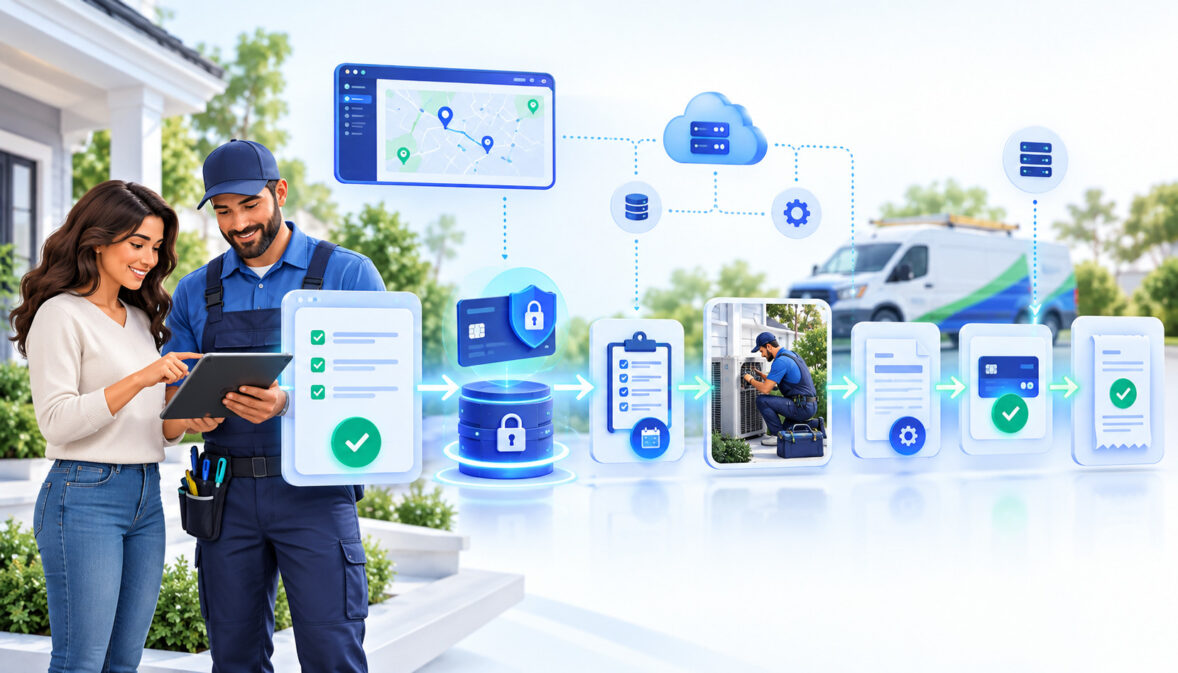
For field-service businesses, the key is to connect payment consent to the actual job workflow: estimate approval, card storage, change orders, job completion, final invoicing, payment initiation, and record retention. Saving a card is not unlimited permission to charge it.
Card on File Authorization for Field Service: What You Need Before Charging
A field-service company should obtain the customer’s stored-credential agreement before saving the payment credential or initiating qualifying future charges.
Visa’s current rules require the cardholder agreement to be completed in writing before the credential is stored. Mastercard’s public Transaction Processing Rules similarly tell acquirers to ensure merchants retain the cardholder’s written credential-on-file agreement.
A practical authorization record should cover:
- customer and merchant identity;
- services or work orders covered;
- permission to store the payment credential;
- amount or method used to determine the amount;
- fixed frequency or triggering event, as applicable;
- cancellation and refund terms;
- agreement duration or expiration where applicable;
- how changes will be communicated;
- customer acknowledgment and acceptance time; and
- a retrievable copy of the authorization.
NETWORK REQUIREMENT: Follow Visa/Mastercard stored-credential agreement and transaction-classification rules.
PROCESSOR/ACQUIRER REQUIREMENT: Your gateway must transmit the appropriate stored-credential, CIT, MIT, recurring, installment, or UCOF information.
OPERATIONAL BEST PRACTICE: Link the consent record to the exact estimate, work order, change orders, invoice, and transaction.
Stored Credential Consent Form: What the Networks Actually Require
A stored credential consent form needs to say substantially more than “customer agrees to keep card on file.”
Visa’s current Core Rules for transactions using stored credentials require the merchant to establish the applicable cardholder agreement before the credential is stored and address how future stored-credential transactions are processed.
For variable field-service invoices, the agreement can describe how the transaction amount will be determined rather than treating the stored card as open-ended charging authority.
| Agreement item | Why it matters | Fixed service plan | Variable job total |
| Merchant identity | Identifies who may charge | Company name/contact | Company name/contact |
| Services covered | Limits scope | Maintenance plan | Identified job/work order |
| Credential use | Explains storage/use | Future plan charges | Post-job invoice |
| Amount | Defines authorization | Fixed price | May not yet be known |
| Calculation method | Controls variability | Usually unnecessary | Estimate + approved changes + tax |
| Frequency | Defines schedule | Monthly/quarterly, etc. | Usually not scheduled |
| Triggering event | Defines when merchant may act | Billing date | Job completion/final invoice |
| Cancellation/refund | Defines customer rights/process | Required terms | Applicable service/refund terms |
| Expiration | Limits agreement where applicable | Plan term | Job-specific end point |
| Authorization record | Provides evidence | Retained acceptance | Retained acceptance |
Do not assume every row is worded identically by every card network. Visa and Mastercard also use different transaction terminology.
Cardholder-Initiated vs Merchant-Initiated Transactions
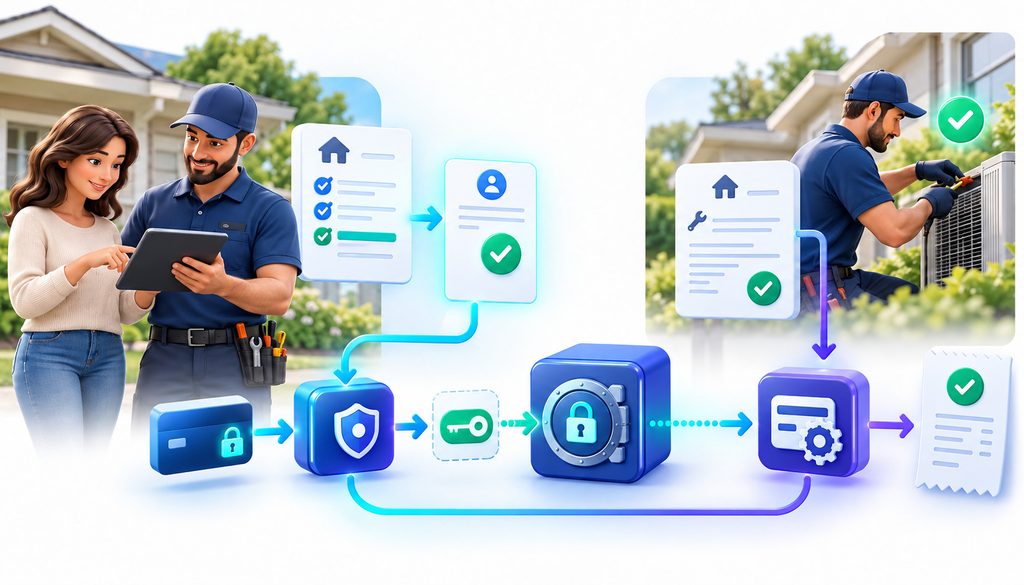
A cardholder-initiated transaction, or CIT, involves the customer actively initiating the payment interaction. A merchant-initiated transaction, or MIT, is initiated by the merchant under a prior agreement without the customer actively participating in that specific transaction.
| Issue | CIT | MIT |
| Who initiates it? | Customer | Merchant |
| Customer actively participating? | Yes | Not in that specific charge |
| Field-service example | Customer taps Pay or submits card during estimate approval | Company charges after agreed completion event |
| Basis | Current customer action | Prior stored-credential agreement |
| Payment messaging | CIT/stored-credential indicators as applicable | Appropriate MIT classification |
| Key evidence | Customer action + transaction | Prior agreement + triggering event + invoice |
For example, a homeowner may approve an HVAC estimate on a tablet and actively establish the stored-card relationship. Several days later, the company may initiate the agreed post-completion charge without the homeowner pressing Pay again.
Typing a stored card number manually does not magically turn a transaction into a compliant MIT.
Why the Setup Transaction Matters
The first interaction establishes the stored-credential relationship.
Visa requires a written cardholder agreement and, before storing the credential, either an authorization request for the transaction amount when payment is due or an Account Verification when no payment is required. If that initial authorization or verification is not approved, Visa says the merchant must not store the credential.
The first interaction therefore is not automatically an MIT.
Mastercard likewise distinguishes original cardholder-initiated credential-on-file transactions from subsequent merchant-initiated transactions. Its public rules use C-series identifiers for the initial CIT and M-series classifications for later MIT activity.
For recurring and installment transactions, Mastercard’s public TPR also contains an April 17, 2026 recommendation for economically related Transaction Link Identifier data connecting later transactions to the original CIT. Merchants normally depend on their gateway/acquirer to implement these technical fields.
Which Stored-Credential Model Fits the Field-Service Job?
Not every saved-card charge is “recurring.”
| Field-service billing model | Visa terminology | Mastercard terminology | Example |
| One approved job; later event-triggered charge | UCOF | M101 UCOF for qualifying later MIT | HVAC replacement |
| Irregular future service calls | UCOF | M101 UCOF | Plumbing account |
| Fixed frequency, variable amount | Recurring | M102 Standing Order | Monthly commercial maintenance |
| Fixed frequency, fixed amount | Recurring | M103 Subscription | Maintenance membership |
| Fixed project installments | Installment | C104 initial / M104 later | Equipment installation |
Visa defines a UCOF transaction as a fixed- or variable-amount stored-credential transaction that does not occur on a scheduled or regularly occurring date and that the merchant initiates with the cardholder’s consent. Its recurring category, by contrast, involves transactions at fixed, regular intervals.
The software provider or acquirer should validate the exact classification for its implementation.
How Do You Authorize a Card When the Final Job Total Can Change?
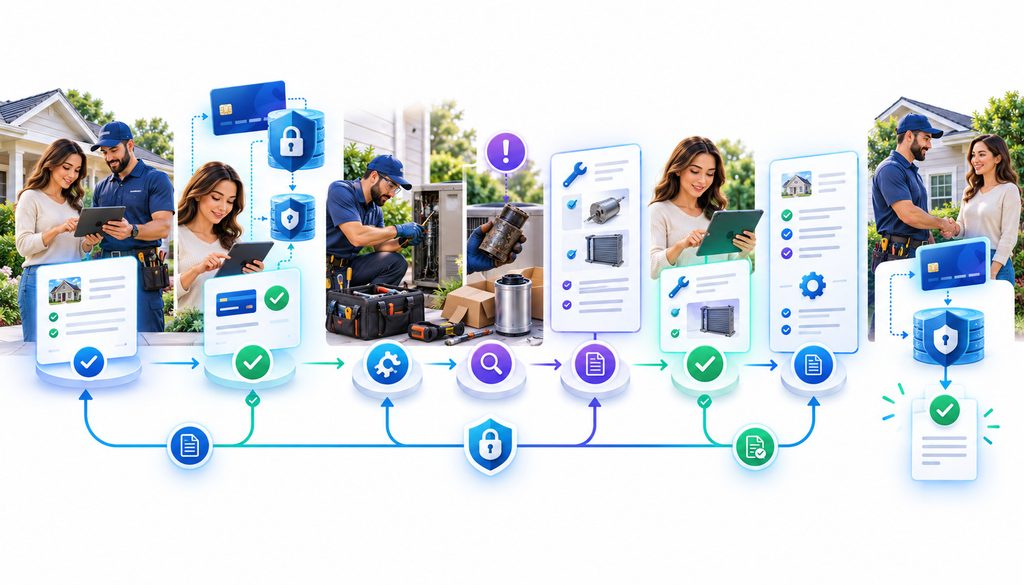
A variable service invoice does not need to become an open-ended authorization.
Visa expressly permits the agreement to contain either the transaction amount or a description of how the amount will be determined. That is particularly useful in field service, where labor, materials, tax, and approved changes may alter the final invoice.
A defensible pricing basis might be:
- the approved estimate plus customer-approved change orders;
- published hourly labor plus documented materials;
- the signed work order plus applicable taxes and disclosed fees; or
- the final invoice generated according to the pricing terms in the service agreement.
“Charge whatever amount we decide” provides weak evidence and invites disputes.
An amount cap can be an additional contractual safeguard, but there is no basis here for claiming that every network universally requires an “amount range.”
What an Auto-Charge Clause Should Cover for a Variable Job Total
Estimate approval and payment authorization should tell the same story, but they are not the same thing.
A customer who approves “replace the compressor for the quoted price” has approved the work. That statement alone does not necessarily establish permission to store a card and initiate a later transaction.
Card-on-File Agreement Template Contents
The authorization workflow should identify:
- company and customer;
- property or service location;
- estimate/work-order reference;
- permission to store a tokenized credential;
- services covered;
- how the amount will be calculated;
- approved-change-order treatment;
- charging trigger;
- any agreed pre-charge notification;
- invoice-dispute procedure;
- cancellation and refund terms;
- revocation method;
- duration; and
- customer acknowledgment and date.
That is clause anatomy, not a universal legal form.
How to Capture Card-on-File Consent at the Customer’s Property
The strongest field workflow creates an affirmative, retrievable record, particularly when the company already uses digital field-service workflows for customer signatures, job records, and on-site or post-job payment collection. Payment consent should become another documented part of that same job record rather than a separate note that billing staff must reconstruct later.
Checkbox at Estimate Approval
Use an unchecked box that the customer must actively select. Store the disclosure version, checkbox state, timestamp, customer identity, work-order ID, authorization text, and processor token reference.
A checkbox should not be described as universally sufficient without confirming applicable law and processor/acquirer requirements.
E-Signature or Customer Portal
An electronic agreement can produce a strong audit trail because the accepted text, signer, time, job, and credential reference can remain together.
A signature does not fix vague payment terms. The customer still needs to understand what future use is being authorized.
Recorded Phone Authorization
Treat a recording as supporting evidence, not a universal replacement for a written Visa/Mastercard stored-credential agreement.
Businesses also need a lawful call-recording process under applicable federal and state rules. And if card data is captured on recorded calls, PCI controls matter: PCI SSC specifically prohibits retaining card verification codes in voice recordings after authorization.
Do not confuse this issue with Nacha’s separate ACH telephone-authorization framework.
[Expert Quote Placeholder: Insert a verified quote from a payments/acquiring specialist explaining why the customer’s original agreement, final invoice, and transaction classification all need to tell the same story.]
Merchant-Initiated Transaction Field Service Workflow
A practical merchant initiated transaction field service process can work like this:
At Estimate Approval
- Customer reviews the estimate.
- Customer reviews the stored-card authorization.
- Customer actively accepts it.
- Customer e-signs or otherwise creates the required written/electronic record.
- Payment provider validates the credential and tokenizes it.
- Authorization record is attached to the job.
During Work
- Technician records labor and materials.
- Additional scope requires documented customer approval.
- Approved change orders update the final-price calculation.
At Completion
- Technician marks the job complete.
- System generates the final invoice.
- Software checks the invoice against approved scope and changes.
- Customer receives the invoice or agreed pre-charge communication.
- Payment integration submits the correct transaction classification.
- Receipt is sent.
- Agreement, work order, changes, invoice, notifications, and payment remain linked.
The merchant should not mark every stored-card transaction as an MIT merely to avoid authentication or improve approval rates. Classification must reflect what actually occurred.
Send the Invoice Before the Charge Becomes a Surprise
Do not invent a universal U.S. “48-hour” or “three-day” advance-notice requirement for ordinary field-service card-on-file transactions.
NETWORK REQUIREMENT: Follow any transaction-specific or regional notice rules that actually apply.
LEGAL REQUIREMENT: Applicable state or federal law may add obligations.
BEST PRACTICE: For a variable post-service charge, send the completed-work summary, final invoice, authorized changes, expected amount, charging date, and customer-service contact before the transaction where operationally practical.
That reduces disputes involving unrecognized amounts, missing change orders, or a customer who believed another payment step was required. Notice does not cure a charge that was never authorized.
Some businesses instead require the customer to press “Pay” after every job. That adds friction but creates a new CIT. Others rely on a prior event-triggered authorization and submit a qualifying MIT. Neither structure should be treated as universally preferable.
Auto-Charge Customer Card Rules: Do and Don’t
| Do | Don’t |
| Obtain consent first | Save a card without permission |
| Define amount/calculation | Use blank-check language |
| Define schedule or event trigger | Treat estimate approval as unlimited payment consent |
| Document change orders | Charge materially expanded work without approval |
| Tokenize credentials | Store CVV or put PAN in technician notes |
| Honor revocation | Keep initiating charges after valid revocation |
| Send invoices and receipts | Manipulate MIT indicators manually |
These auto charge customer card rules combine network requirements with operational controls; they are not all independent statutes.
Recurring Service Payment Authorization
A true recurring service payment authorization is appropriate for regular service arrangements such as pool maintenance, pest control, lawn care, commercial cleaning, or an HVAC membership.
Visa defines recurring transactions as a series processed at fixed, regular intervals. Mastercard uses its own stored-credential classifications rather than simply calling every future charge “recurring.”
Its Transaction Processing Rules for credential-on-file and merchant-initiated transactions distinguish categories such as Unscheduled Credential-on-File and other qualifying merchant-initiated payment patterns. The processor or gateway should transmit the classification that matches what actually happened.
A one-time repair followed by a post-completion charge should not be mislabeled as a subscription simply because the card was stored.
Card-on-File Authorization Is Not the Same as ACH Authorization
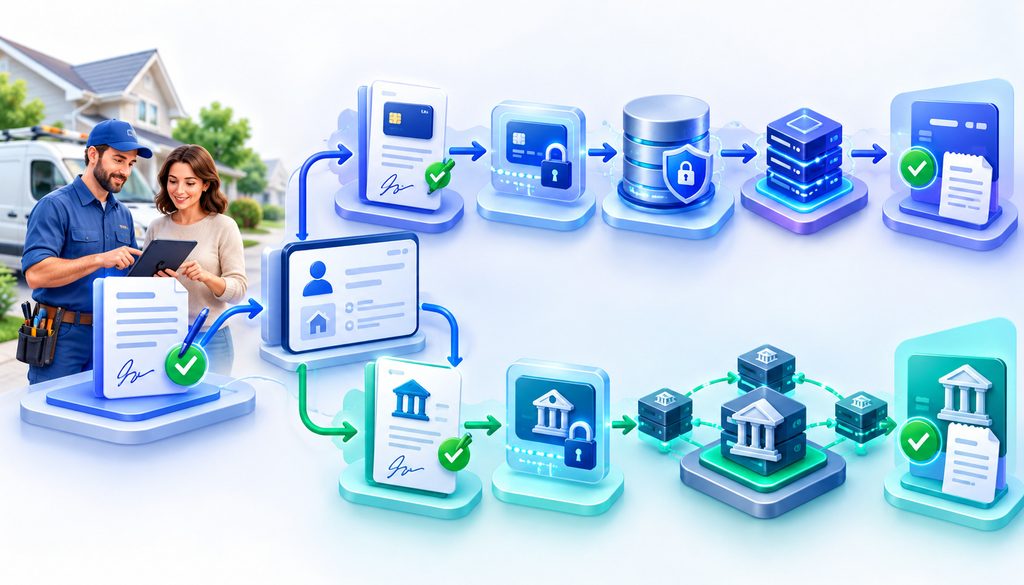
Card consent does not automatically authorize ACH, and ACH consent does not automatically authorize card charges.
| Issue | Card on file | ACH debit |
| Governing payment rules | Card network + acquirer | Nacha; Regulation E for covered consumer EFTs |
| Authorization | Stored-credential agreement | Depends on SEC code; consumer preauthorized EFTs require writing/similar authentication under Reg E |
| Variable amount | Network agreement may define calculation method | Reg E generally requires advance varying-amount notice, subject to permitted range/difference alternatives |
| Date changes | Depends on card arrangement/rules | Nacha guidance specifies notice requirements |
| Revocation | Stored-card agreement/network process | ACH authorization/stop-payment framework |
| Proof | Agreement + transaction/job records | Originator must retain/provide authorization evidence |
| Dispute system | Card-network disputes | ACH returns/EFTA rights as applicable |
| Storage | Prefer processor token | Protect bank-account credentials appropriately |
Card-on-file consent should not simply be reused as ACH authorization. For covered consumer preauthorized transfers, Regulation E §1005.10 requires a writing signed or similarly authenticated by the consumer, and the person obtaining the authorization must provide the consumer with a copy. The regulation also contains separate provisions for varying recurring debit amounts.
For varying amounts, §1005.10 generally requires notice at least 10 days before the scheduled transfer, while permitting an agreed range or difference-based alternative.
Nacha’s current developer guidance separately describes seven-calendar-day notice for a debit-date change and 10-calendar-day notice for an amount change, plus SEC-code-specific proof requirements.
What Field Service Software Should Store With the Authorization
Field-service software should store authorization evidence alongside the same work orders, customer sign-offs, job notes, estimates, billing, and invoicing records that document the rest of the service lifecycle, rather than storing unnecessary raw card data.
Useful fields include customer and property IDs; estimate/work-order ID; authorization ID and version; timestamp and acceptance method; immutable authorization text; covered services; pricing calculation method; schedule or event trigger; cancellation status; processor customer/payment-token references; initial setup transaction or verification reference; later transaction IDs; invoices; change orders; receipts; and notification history.
A payment provider should normally tokenize the credential so technicians and ordinary application logs never need the full PAN.
Build the Authorization Record So You Can Find It in Minutes
If the customer says, “I never authorized this charge,” the business should be able to assemble a dispute packet quickly:
- stored-credential agreement and exact version;
- consent timestamp and identity record;
- estimate and work order;
- approved change orders;
- job-completion record;
- final invoice;
- pre-charge communication, if sent;
- payment receipt and processor transaction ID;
- proof of service;
- relevant customer communications; and
- cancellation or revocation history.
Good evidence does not guarantee a chargeback win, but keeping customer approvals, job documentation, invoicing records, and payment events inside a centralized service-business workflow with documentation logs and audit trails can make the underlying transaction much easier to reconstruct when a dispute arrives.
A Stored Card Does Not Eliminate Change-Order Approval
Discovering extra work does not create a blank check.
Record the original scope, added work, price difference or revised calculation, customer approval, and timestamp. Emergency fees, trip charges, disposal fees, upgraded parts, permits, taxes, and similar additions should also fit the disclosed pricing basis.
The card-on-file agreement should support the agreed payment process; it should not replace ordinary scope approval.
What Happens When the Customer Revokes Card-on-File Authorization?
Canceling card-on-file authority and disputing the underlying debt are separate issues.
A customer might revoke stored-card permission, cancel a maintenance plan, replace the payment method, dispute work already performed, or dispute an already completed card transaction. Those events have different consequences.
An outstanding invoice does not by itself mean the merchant may keep attempting a credential whose future use has been validly revoked. The business can preserve the receivable while using another legitimate collection method.
If the Merchant-Initiated Charge Declines
Do not blindly retry a declined MIT indefinitely.
Visa’s April 2026 rules state that after a declined merchant-initiated stored-credential authorization, the merchant must notify the cardholder in writing and allow at least seven calendar days to pay by other means.
Mastercard uses Merchant Advice Codes on declining recurring authorizations and expects the downstream parties to act on that advice. Follow the gateway/acquirer’s current retry and response-code logic rather than inventing a retry schedule.
PCI DSS, Tokenization, Receipts, and Descriptors
Use a PCI-compliant provider and tokenization rather than copying payment cards into technician notes, PDFs, emails, or ordinary application fields.
PCI DSS prohibits retaining CVV/CVC after authorization, even if the customer says it is okay and even if the value is encrypted.
Receipts should make the transaction recognizable: use the merchant name customers know, job or invoice reference where appropriate, service description, amount, date, and support contact. Do not place sensitive personal information in card descriptors.
Disputes become more likely when the final total materially exceeds expectations, change orders are undocumented, the customer misunderstood the charging trigger, the descriptor is unfamiliar, the wrong job is billed, or a credential is used after revocation.
Card-on-File Agreement Template Contents
| Agreement component | Example information | Why it matters |
| Merchant identity | Legal/DBA name and contact | Identifies charging party |
| Customer identity | Customer/cardholder | Connects consent |
| Service scope | Named job or plan | Defines coverage |
| Storage permission | Tokenized credential may be stored | Establishes COF relationship |
| Covered transactions | Completion charge/future calls | Limits future use |
| Amount | Fixed amount when known | Defines authorization |
| Calculation method | Estimate + approved changes | Handles variable invoices |
| Frequency/event | Monthly or completion trigger | Defines initiation |
| Change orders | Customer-approved additions | Documents expanded scope |
| Charge timing | After completion/invoice | Sets expectation |
| Cancellation | Method/contact | Enables termination |
| Refund policy | Applicable service terms | Establishes treatment |
| Revocation | How future card use stops | Separates payment authority |
| Expiration | Plan/job term | Limits duration |
| Credential identifier | Last four/token reference | Identifies payment method |
| Acceptance record | Version + timestamp | Provides evidence |
Hypothetical: A Better HVAC Workflow
An HVAC company quotes a replacement job at $3,800. The homeowner electronically approves the estimate and card-on-file terms, which state that the final invoice equals approved work plus customer-approved changes and tax.
During the job, the homeowner electronically approves a $325 replacement part. After completion, the system creates the final invoice, sends it to the homeowner, initiates the agreed stored-credential payment, and retains the estimate, consent, change order, completion record, invoice, receipt, and transaction ID.
Contrast that with copying a card from an old invoice, obtaining no current payment agreement, approving added work only verbally, charging $4,600, and sending the invoice afterward. The second workflow creates substantially weaker authorization and amount evidence.
Common Card-on-File Myths
| Myth | Reality |
| “They gave me the card once, so I can keep charging it.” | Prior card use is not unlimited authority. |
| “Estimate approval authorizes the later charge.” | Work approval and stored-payment consent are distinct concepts. |
| “All card-on-file payments are recurring.” | UCOF, recurring, installment, CIT, and MIT differ. |
| “The first transaction is always an MIT.” | Initial customer setup may be a CIT or verification interaction. |
| “A recorded call always satisfies the networks.” | Do not assume voice alone replaces required written COF terms. |
| “A signature lets me charge any amount.” | Amount or calculation basis still matters. |
| “Card consent also covers ACH.” | The payment rails require separate authorization analysis. |
| “A technician can just re-key the saved number.” | Stored-credential processing should use the configured COF framework. |
| “Signed consent guarantees a chargeback win.” | Dispute outcomes depend on the facts and network rules. |
Common Field-Service Payment Mistakes
| Mistake | Risk | Better control |
| Vague COF sentence | Scope dispute | Detailed authorization |
| No price methodology | Amount dispute | Defined calculation |
| No change-order trail | Expanded-work dispute | Digital approvals |
| Wrong recurring/MIT classification | Processing problems | Gateway-driven classifications |
| Pre-checked consent | Weak affirmative evidence | Customer action |
| Raw card data in notes | Security/PCI exposure | Tokenization |
| No revocation log | Charges after cancellation | Timestamped status |
| Job/payment records separated | Slow dispute response | Linked job ledger |
Questions to Ask Your Payment Processor or Software Provider
- Does the integration correctly identify the initial credential-on-file setup?
- How are later CITs and MITs classified?
- Does it support Visa UCOF?
- Which Mastercard MIT categories are supported?
- How are variable-amount/fixed-frequency payments classified?
- How is the original transaction linked to later MIT activity?
- Where is customer authorization stored?
- Can it be exported during a dispute?
- Can the exact disclosure version be retained?
- Are approved change orders linked to the invoice?
- Can customers revoke card-on-file consent?
- Does revocation stop future MIT attempts?
- Is notification history retained?
- Are credentials tokenized?
- Does raw PAN ever enter the field-service application?
- How are declines and Mastercard Merchant Advice Codes handled?
- Can card and ACH authorization records be maintained separately?
A “yes” answer is not proof of compliance. When payments are embedded in field-service software, the underlying payment integration still has to address tokenization, transaction routing, reporting, reconciliation, and PCI responsibilities, while the stored-credential implementation must also be validated against the applicable network, acquirer, and gateway requirements.
FAQs
Can a field-service company keep my card on file and charge it later?
Yes, when the customer has established the required stored-credential agreement and the future transaction fits that authorization. Keeping a credential does not create unlimited charging authority.
The agreement should define what services are covered, how the amount is established, when a charge can occur, and how future use can be canceled or revoked.
What must a card-on-file authorization include?
The exact requirements depend on the network and transaction type. Visa’s current rules address merchant and transaction information plus stored-credential terms such as amount or calculation method, credential use, timing/frequency when applicable, the UCOF trigger, cancellation/refund terms, and expiration where applicable. Mastercard also expects a written credential-on-file agreement.
Is an approved estimate enough to authorize the final card charge?
Not necessarily. Estimate approval proves that the customer accepted the work or price terms. It does not automatically prove that the customer also agreed to have a payment credential stored and later charged without another active payment step. A field-service workflow should make both acknowledgments clear and retain evidence of each.
What is the difference between a cardholder-initiated and merchant-initiated transaction?
A CIT occurs when the customer actively initiates the payment interaction. An MIT occurs later when the merchant initiates a qualifying transaction under a prior agreement without the customer actively participating in that specific charge.
The distinction affects network messaging, issuer treatment, software configuration, and the evidence needed to explain why the merchant initiated the payment.
Can a field-service company charge more than the original estimate?
A stored card is not permission to add undisclosed work. When the final amount can vary, the authorization should explain how it will be calculated. Additional work should be documented through approved change orders or another clear customer-approval mechanism.
Applicable contract law, consumer-protection law, network rules, and processor requirements may also affect a particular transaction.
Is a recorded phone authorization enough to keep a card on file?
Do not assume so. Visa requires the stored-credential agreement to be completed in writing, and Mastercard’s public rules address retention of a written COF agreement. A recording can provide additional evidence, but it should not automatically be treated as a substitute for the required written/electronic record. Call-recording and PCI requirements also apply.
Does the company have to tell the customer before auto-charging the card?
There is not one universal advance-notice period that applies to every U.S. field-service card-on-file transaction. Network rules, subscription rules, processor requirements, contracts, and applicable law can create specific obligations.
Operationally, sending the final invoice, amount, expected charge date, approved changes, and support contact before a variable post-service charge can substantially reduce surprises and disputes.
Is ACH auto-debit authorization the same as card-on-file authorization?
No. Card payments operate under card-network and acquirer rules. ACH debits operate under Nacha rules and, for applicable consumer transfers, Regulation E.
Consumer recurring ACH authorization has its own writing or similar-authentication requirements, notice rules, revocation rights, and evidence requirements. A card-on-file signature should not simply be reused as ACH authorization without separately establishing ACH consent.
What records should field-service software keep for a card-on-file dispute?
Keep the accepted agreement and version, customer identity, timestamp, estimate, work order, approved change orders, completion evidence, final invoice, notifications, receipt, processor transaction identifier, credential token reference, and revocation history.
Those records should be linked to the same job so the business can reconstruct exactly what the customer authorized and what ultimately occurred.
Build Card-on-File Consent Into the Job Workflow
A strong card-on-file authorization field service workflow begins before the credential is stored. Define the services covered, how a variable invoice will be calculated, what event permits charging, and how the customer can cancel or revoke future card use.
Keep work authorization distinct from payment authorization, document change orders, and let the payment integration correctly distinguish CIT, MIT, recurring, installment, and unscheduled credential-on-file transactions.
Tokenize the credential and make the authorization easy to retrieve. The operational test is simple: when a customer questions a charge months later, your team should be able to pull one job record showing the agreement, approved scope, approved changes, final invoice, charging trigger, customer communications, and payment transaction without searching across disconnected systems.